Take control of your third-party cyber risk, continuously.
Attacks increasingly originate from suppliers, service providers and subcontractors. With Egerie, industrialize the qualification, assessment and management of third-party risk (TPRM) with traceability, compliance and efficiency.

60%
of cyber incidents involve a compromised third party (supply chain)
Up to 3 levels
of assessment based on criticality light · standard · in-depth
600+
suppliers mapped
300+
third parties qualified in ~3 months; maps covering up to 600 suppliers


1. Map & Qualify Your Third Parties
The list of third parties is often scattered and unqualified: it's difficult to know which ones are critical and why.
- Centralized and structured third-party register
- Criticality assessment based on concrete criteria (data, exposure, location, etc.).
- Clear prioritization: who to address first, and at what level of requirement.
- Centralized and structured third-party register
- Criticality assessment based on concrete criteria (data, exposure, location, etc.).
- Clear prioritization: who to address first, and at what level of requirement.

2. Tailor Assessments to Criticality Levels
Evaluating all third parties in the same way is too expensive, takes too much time, and obscures major risks.
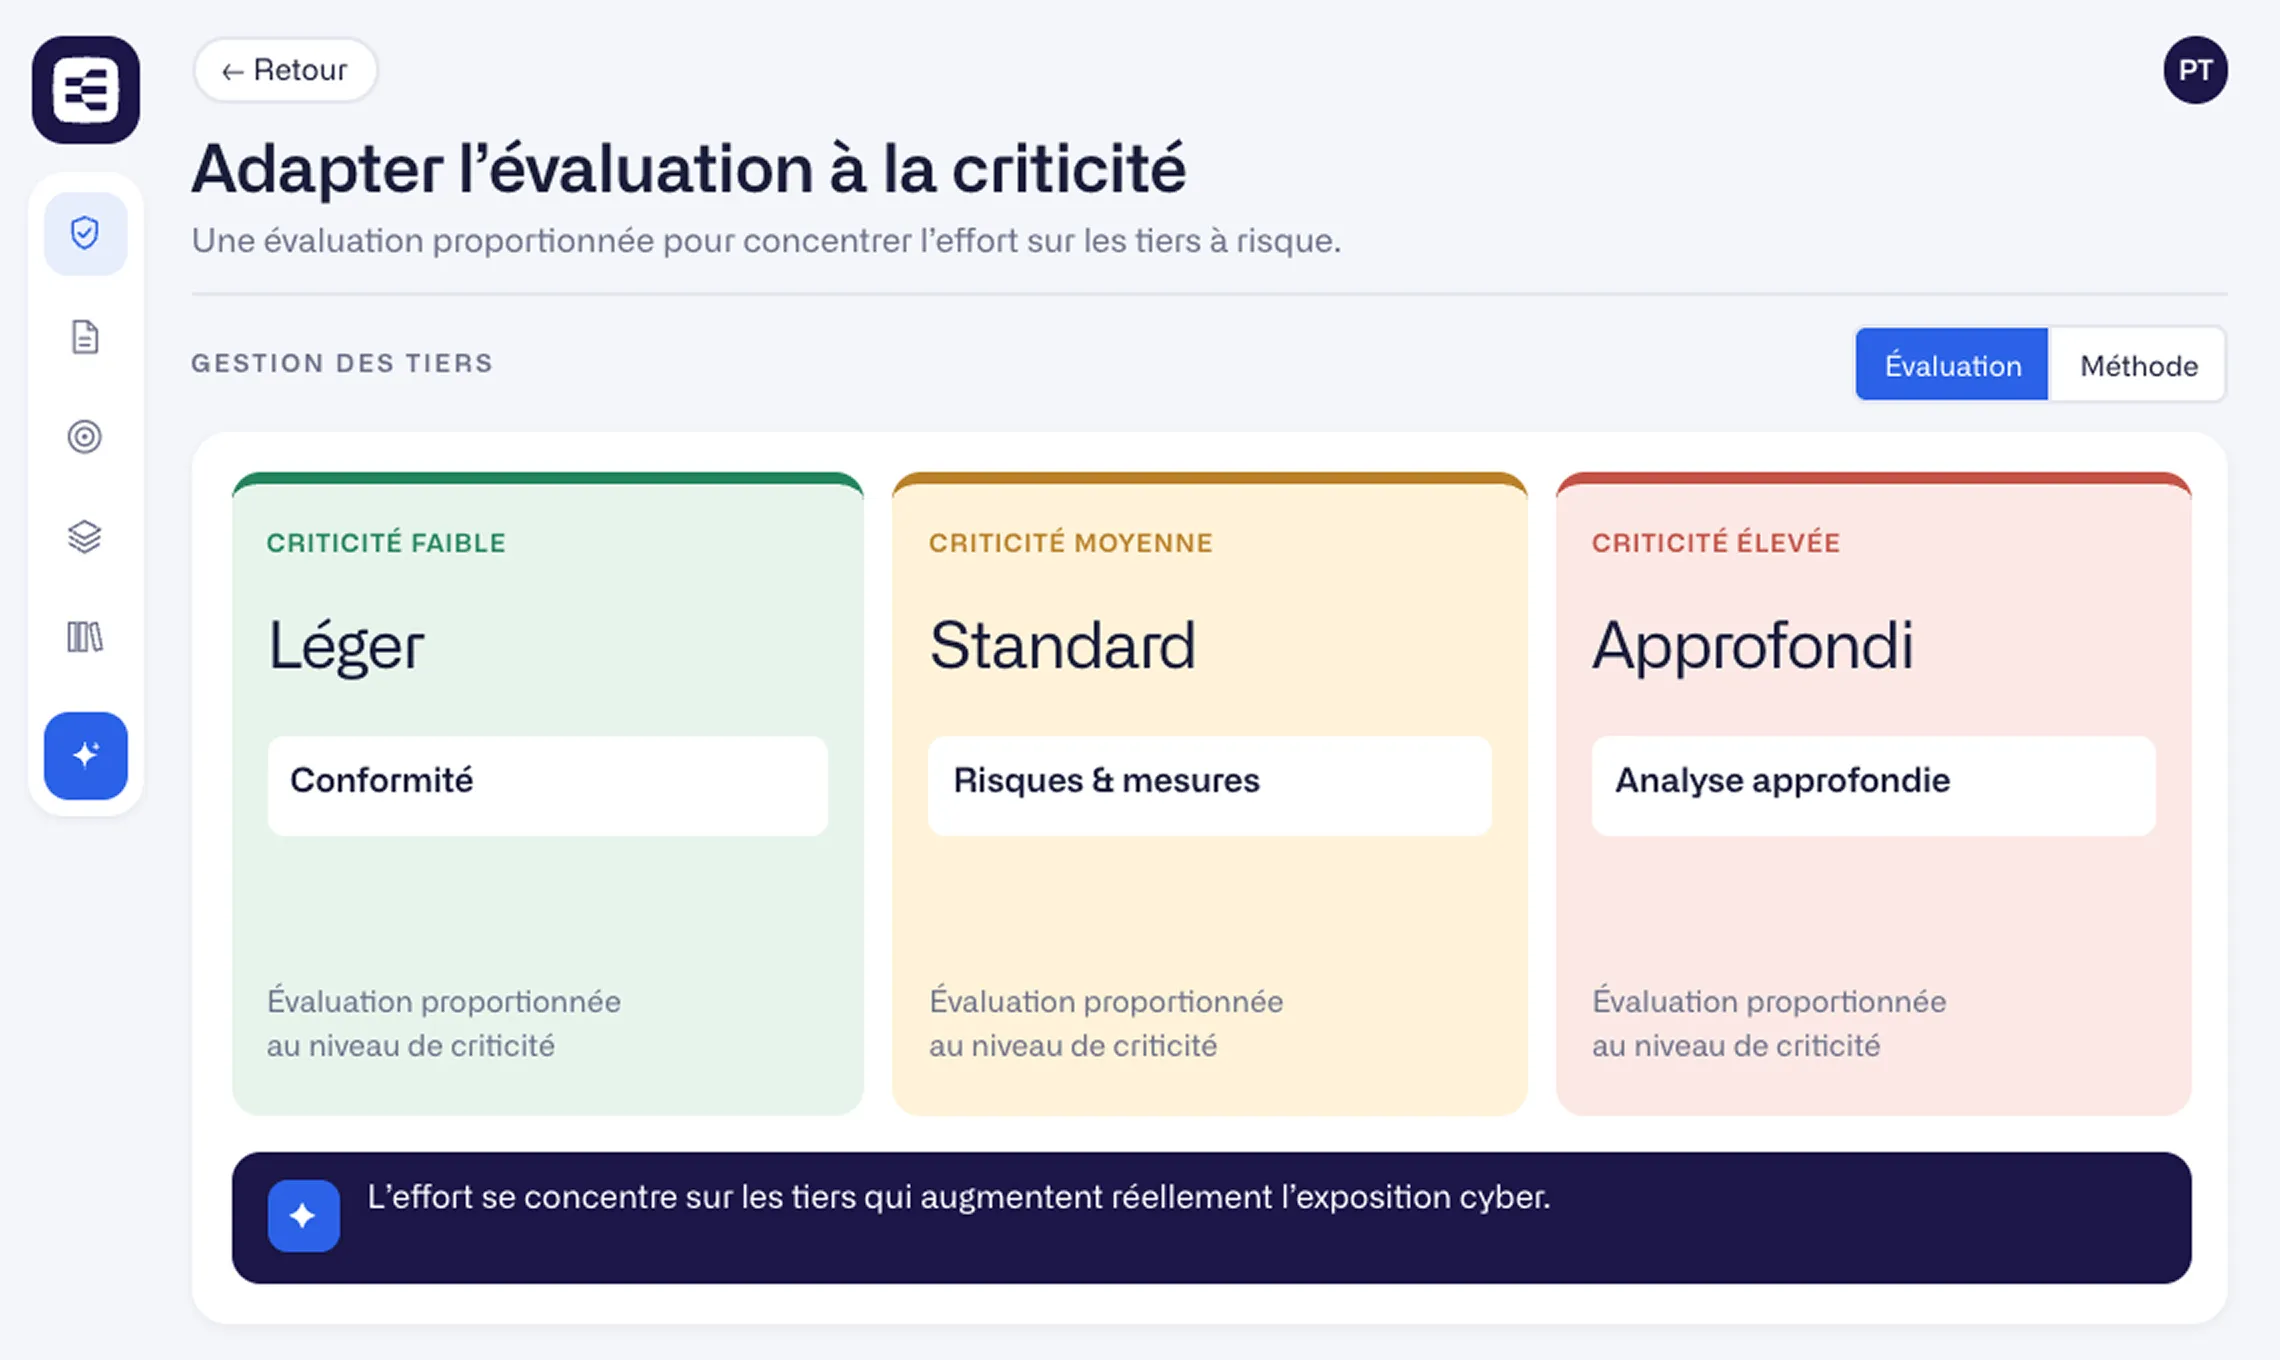
- Proportional assessment: light / standard / in-depth based on criticality.
- Associated method: compliance (low), risks & measures (medium), in-depth analysis (high).
- Effort focused on third parties that genuinely increase cyber exposure.
- Proportional assessment: light / standard / in-depth based on criticality.
- Associated method: compliance (low), risks & measures (medium), in-depth analysis (high).
- Effort focused on third parties that genuinely increase cyber exposure.
3. Standardize Campaigns & Collect Evidence
Manual collection creates delays, endless follow-ups, and evidence that's impossible to find during an audit.
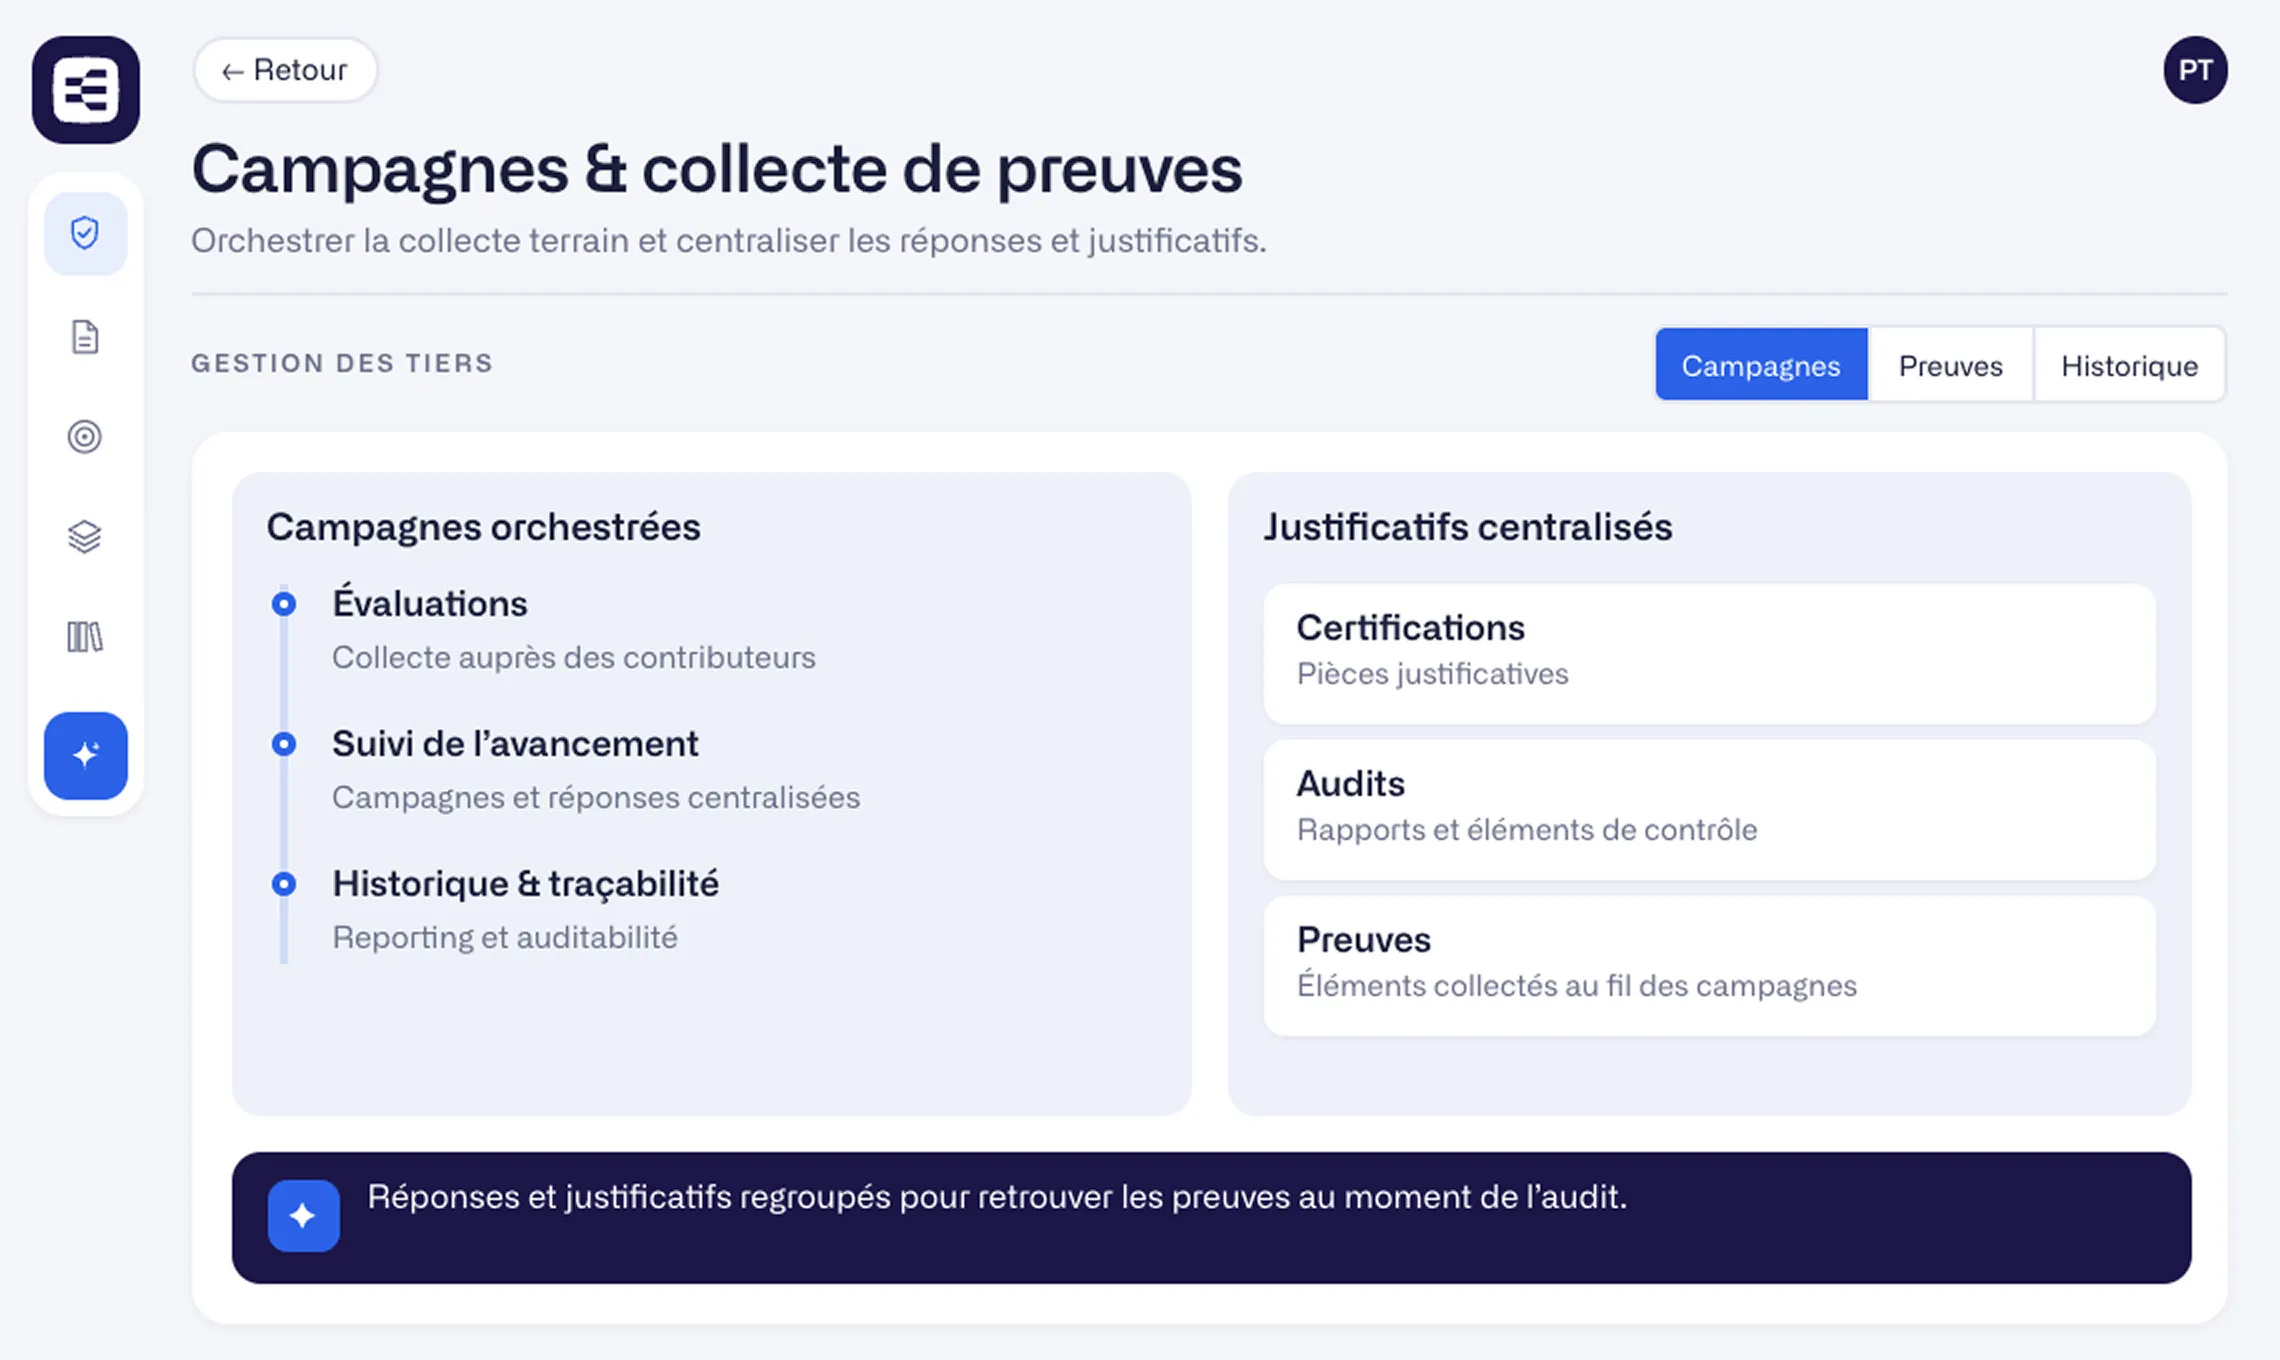
- Orchestrated campaigns with progress tracking.
- Centralized responses and supporting documents (certifications, audits, evidence).
- History and traceability to secure reporting and auditability.
- Orchestrated campaigns with progress tracking.
- Centralized responses and supporting documents (certifications, audits, evidence).
- History and traceability to secure reporting and auditability.
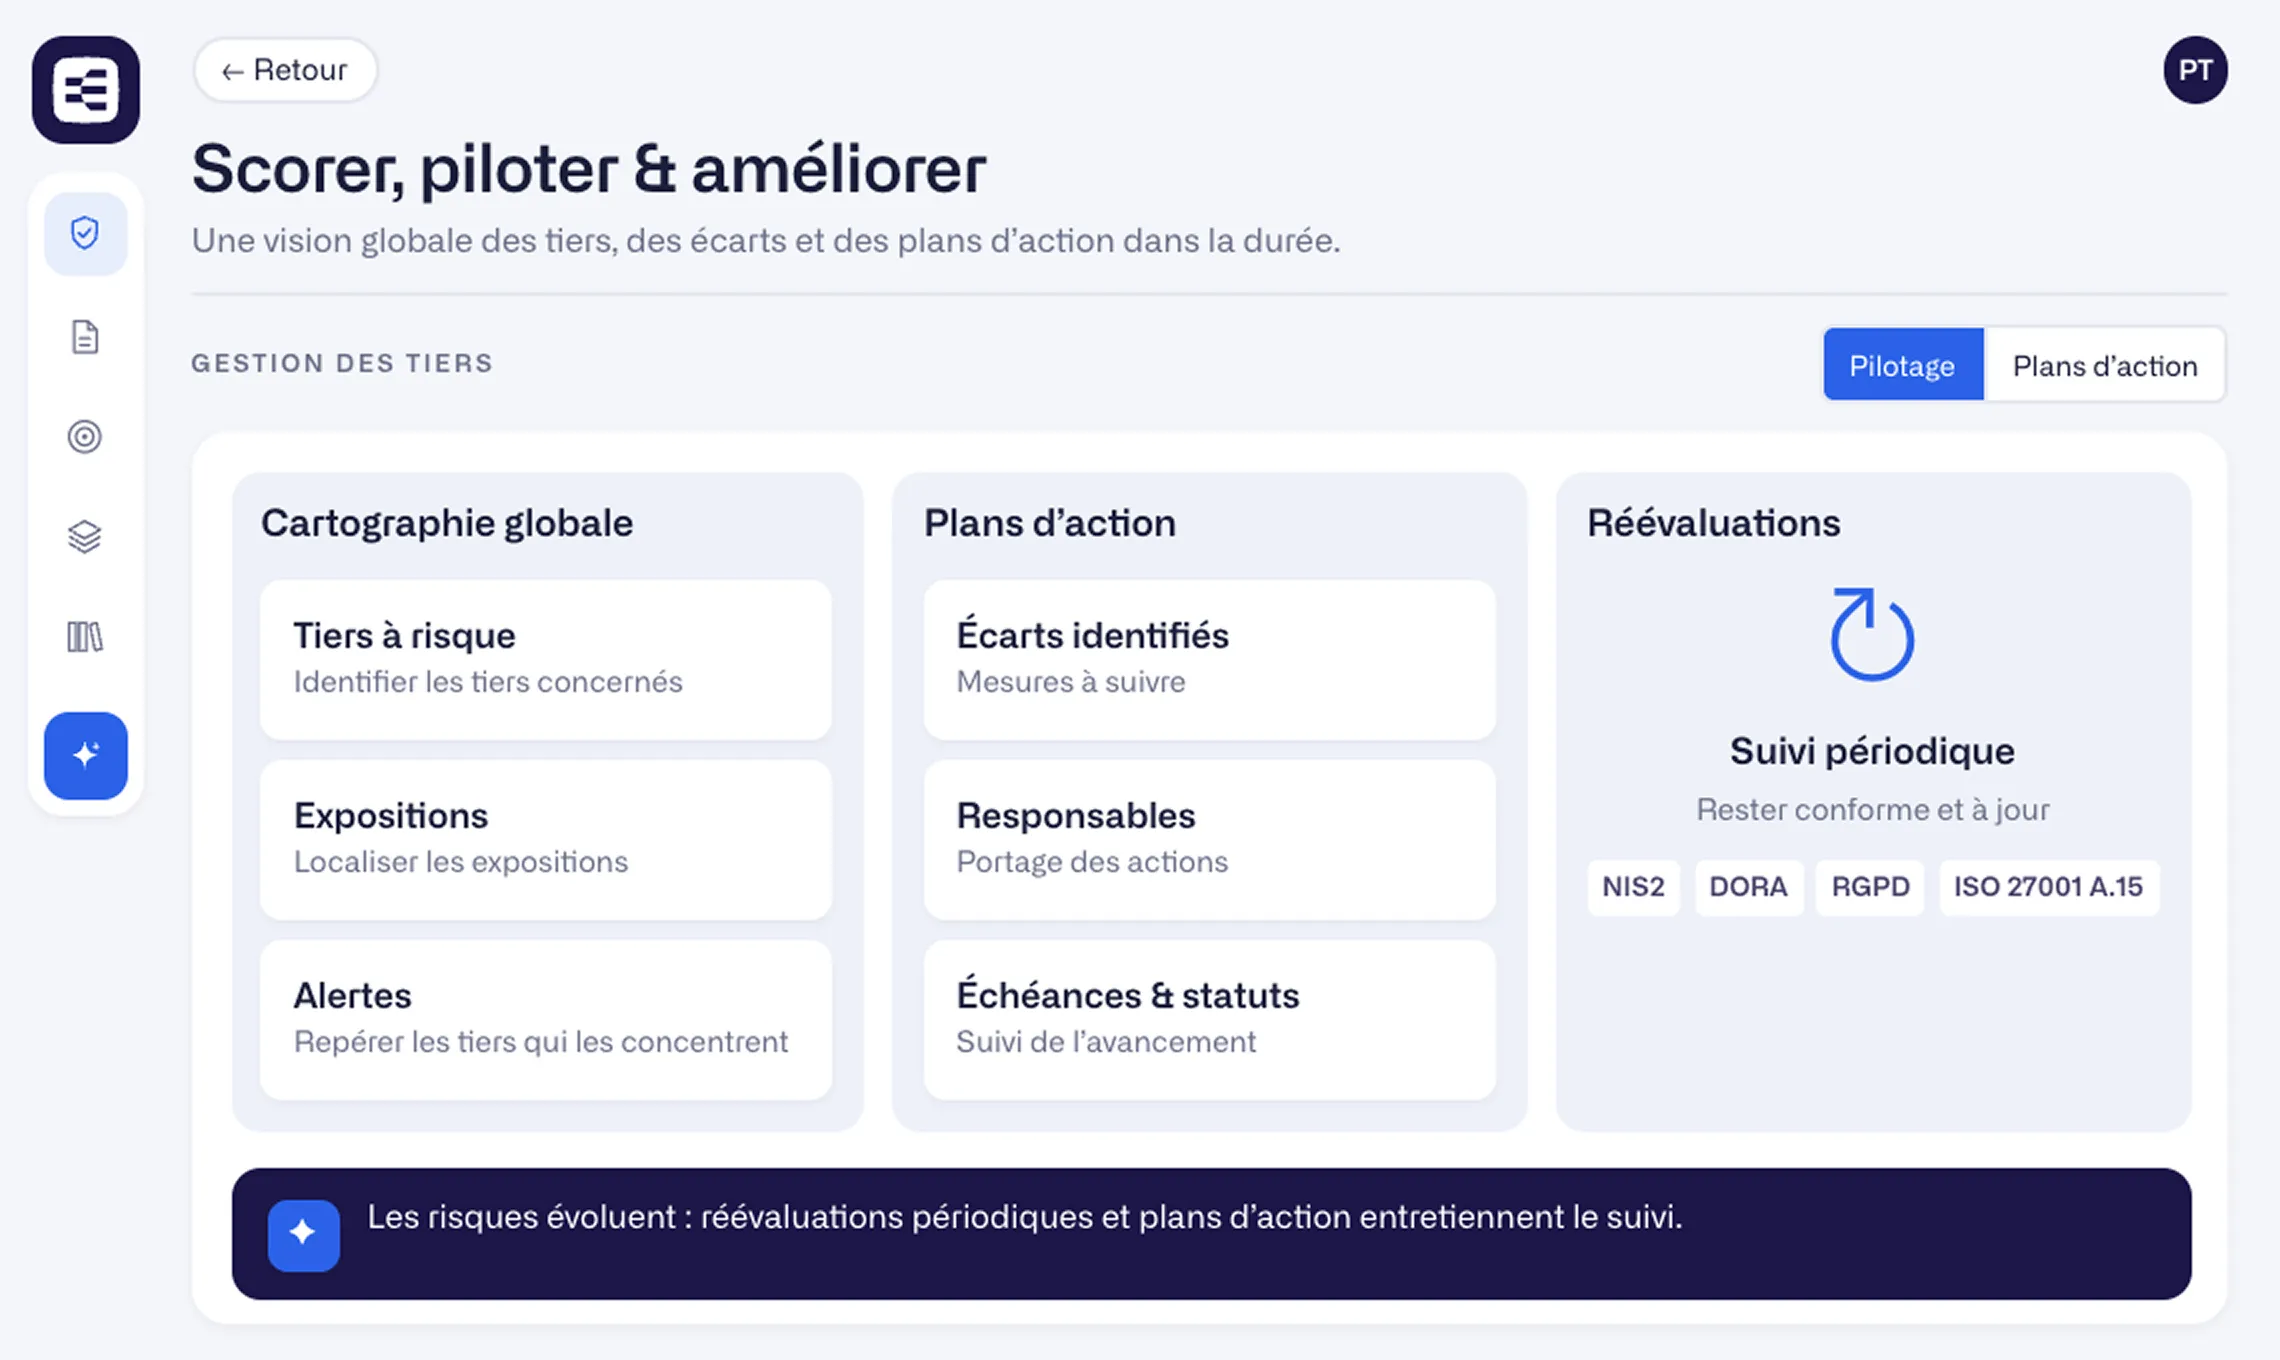
4. Score, Drive & Continuously Improve
Without proper management, evaluation quickly becomes a one-time "snapshot": risks evolve, but monitoring doesn't keep up.
- Global third-party mapping: who is at risk, where exposures are located, and which third parties concentrate the alerts.
- Identified gaps + tracked action plans (owners, deadlines, statuses).
- Periodic re-evaluations to remain compliant and up-to-date (NIS2, DORA, GDPR, ISO 27001 A.15).
- Global third-party mapping: who is at risk, where exposures are located, and which third parties concentrate the alerts.
- Identified gaps + tracked action plans (owners, deadlines, statuses).
- Periodic re-evaluations to remain compliant and up-to-date (NIS2, DORA, GDPR, ISO 27001 A.15).


GAINS
3 measurable gains for your teams

Supply chain risk reduction
Prioritize the third parties that really matter: up to 3 tiers of requirements to focus your effort where exposure is highest.

Industrialized assessment
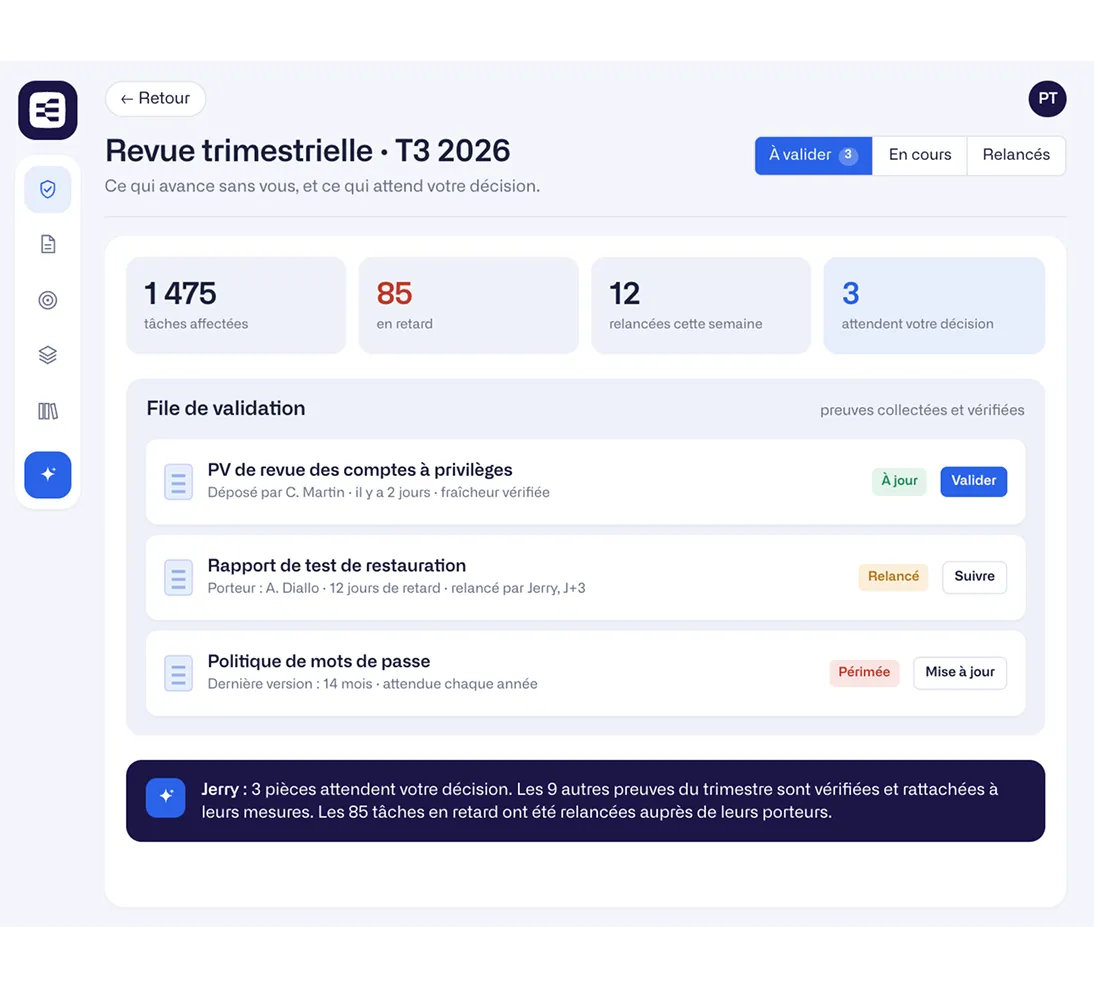
Move from "artisanal" campaigns to an industrialized model: 300+ third parties qualified in ~3 months (field feedback).
Audit-ready (NIS2 / DORA / ISO 27001)
Generate objective, traceable evidence: exchange history, supporting documents, statuses — a solid foundation to demonstrate control over third-party risk.


TESTIMONIALS
Real stories. Real impact.
Every business has its challenges. Learn how our solutions have helped our customers overcome them and strengthen their cybersecurity.




MARKET LEADER
Recognized leader by analysts


