Your compliance structured, managed and audit-ready.

NIS2, ISO 27001, DORA, SecNumCloud: Egerie turns your regulatory obligations into operational action plans. Built for large enterprises and SMEs alike. Deployed in days, not months.

10+
Pre-configured standards ready to use
1000+
Requirements modelled in the library
3600+
Ready-to-use operational tasks
500+
Organizations trust Egerie
EGERIE CONTENT

Our AI-powered technology, validated by experts, that accelerates your compliance.

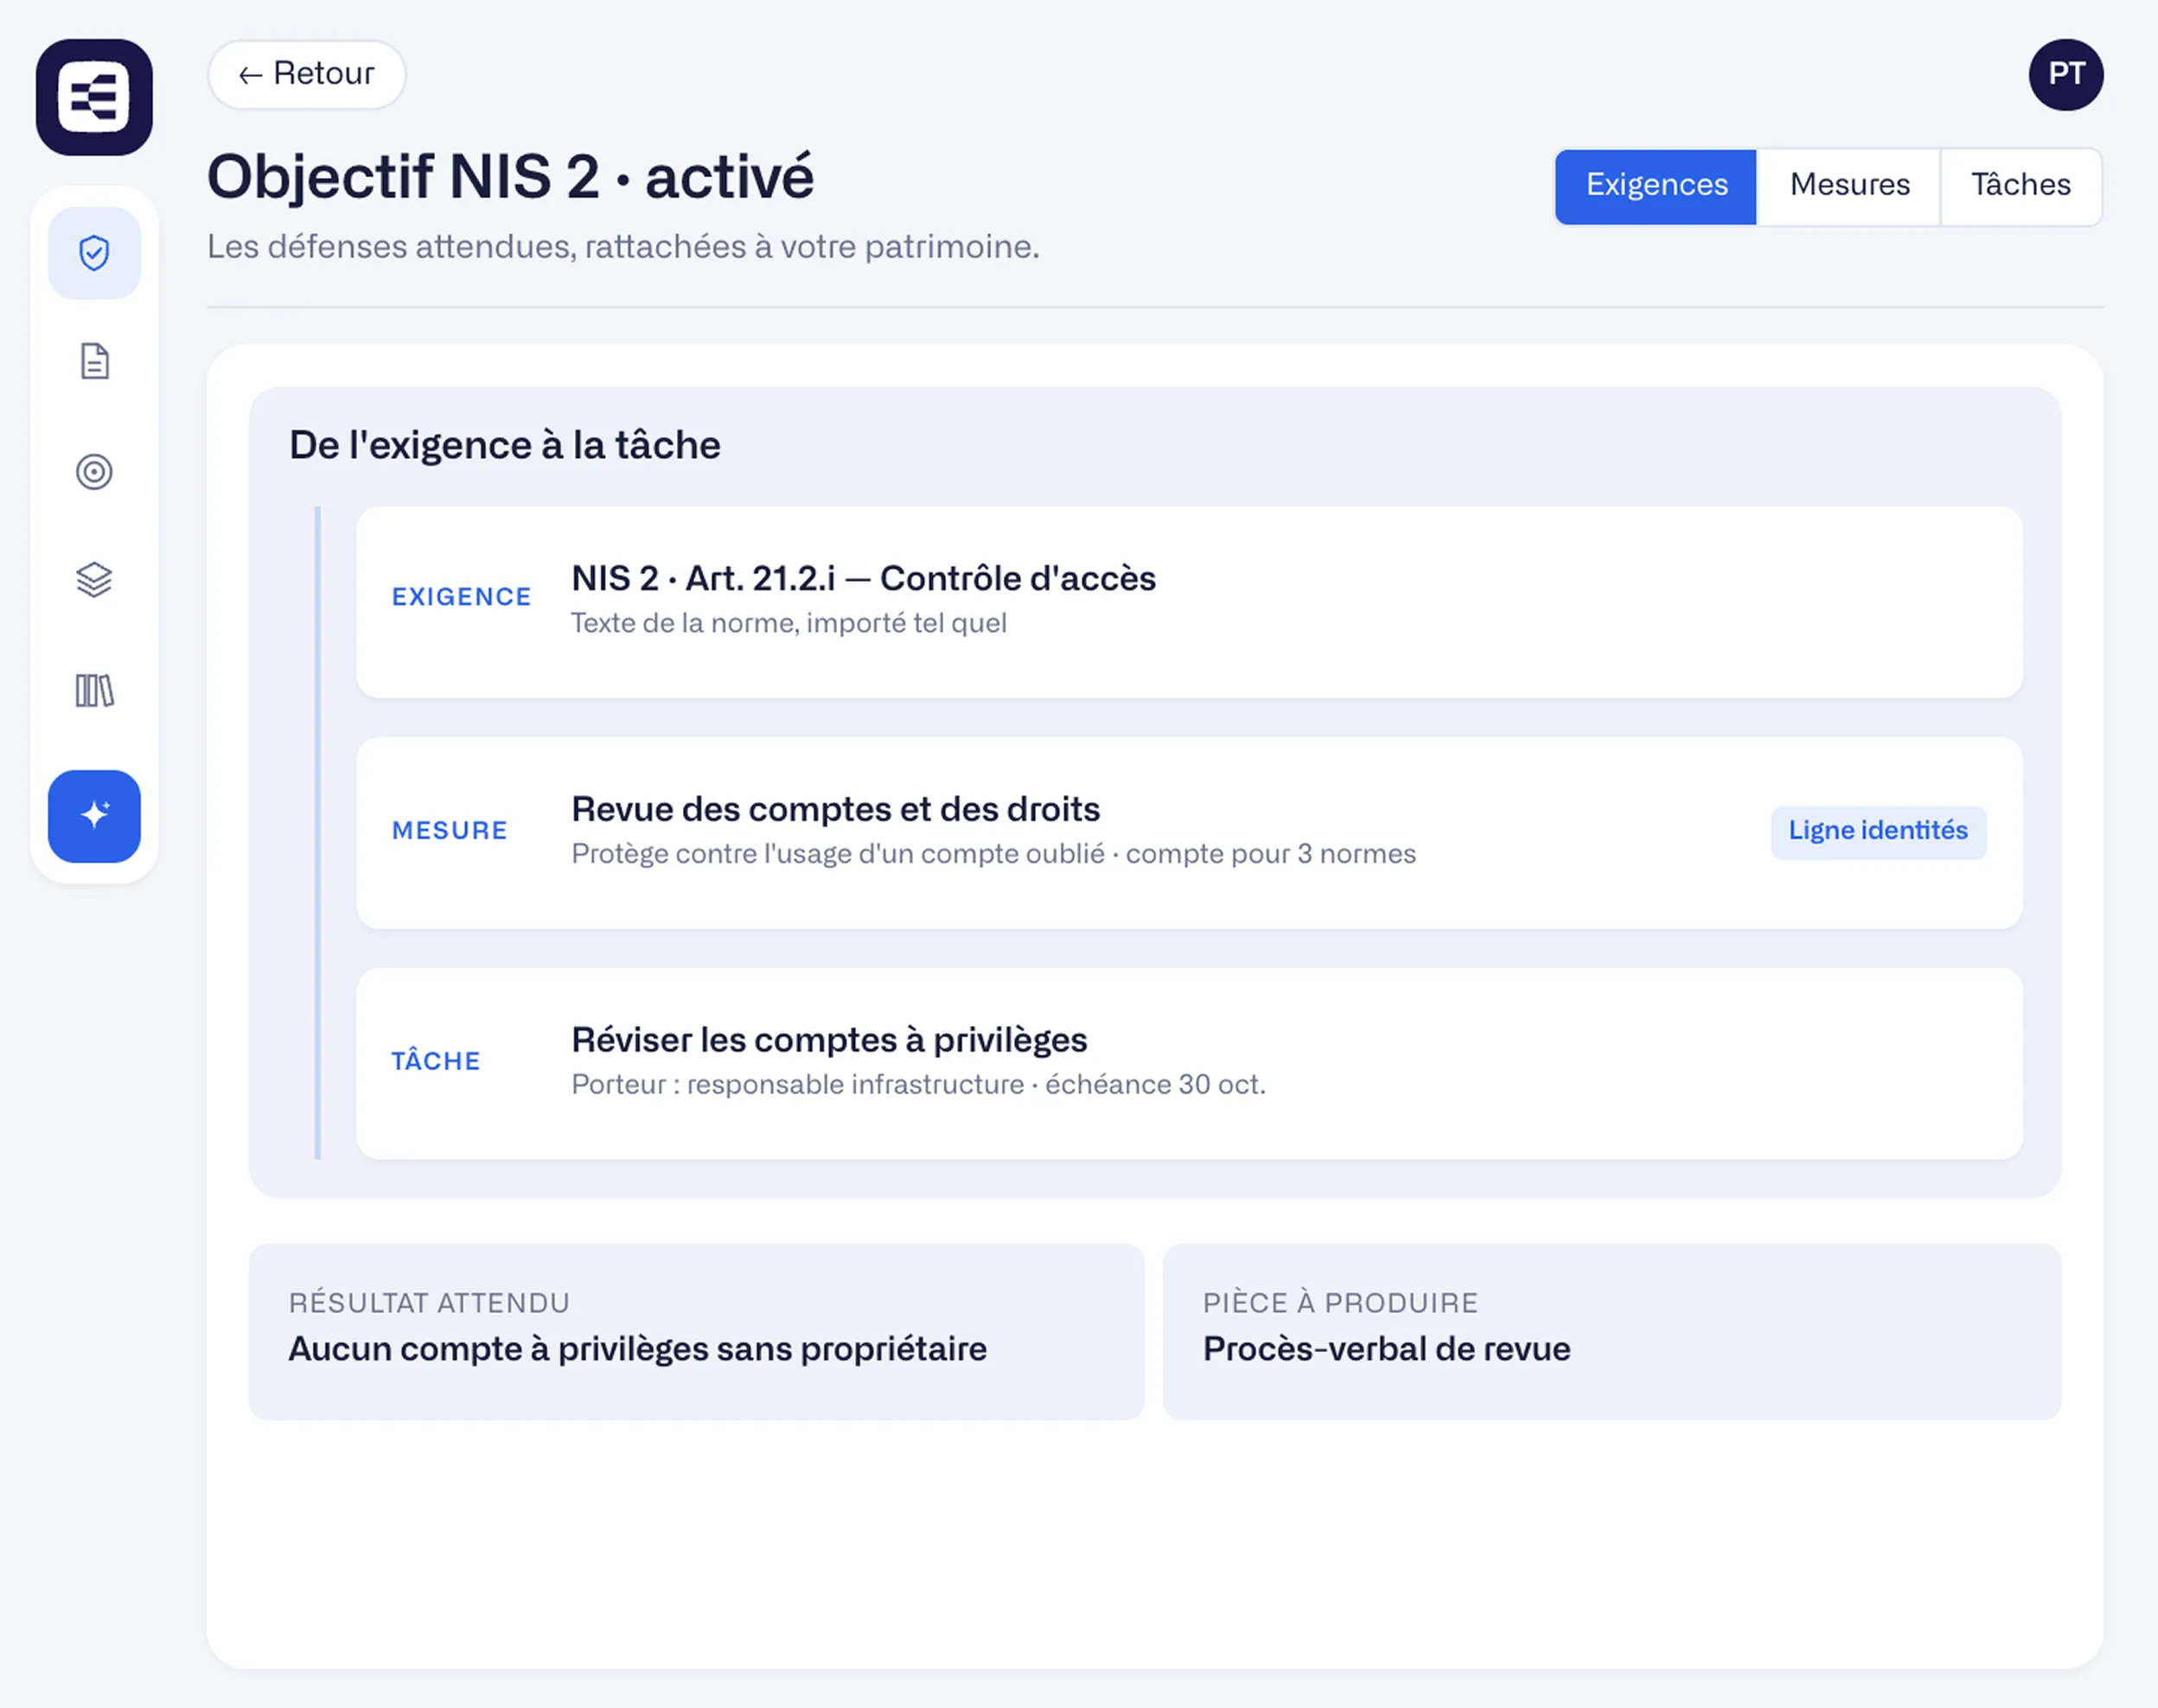
For every requirement in every covered framework, our teams have written the corresponding measure to cover it, the task to carry out, and the expected evidence.

Standard → Requirement → Measure → Task → Evidence

The text of the standard, never rewritten, flows all down to the document to be produced.

One measure counts for multiple frameworks

Maintained for NIS2, it also counts for ISO 27001 and DORA.

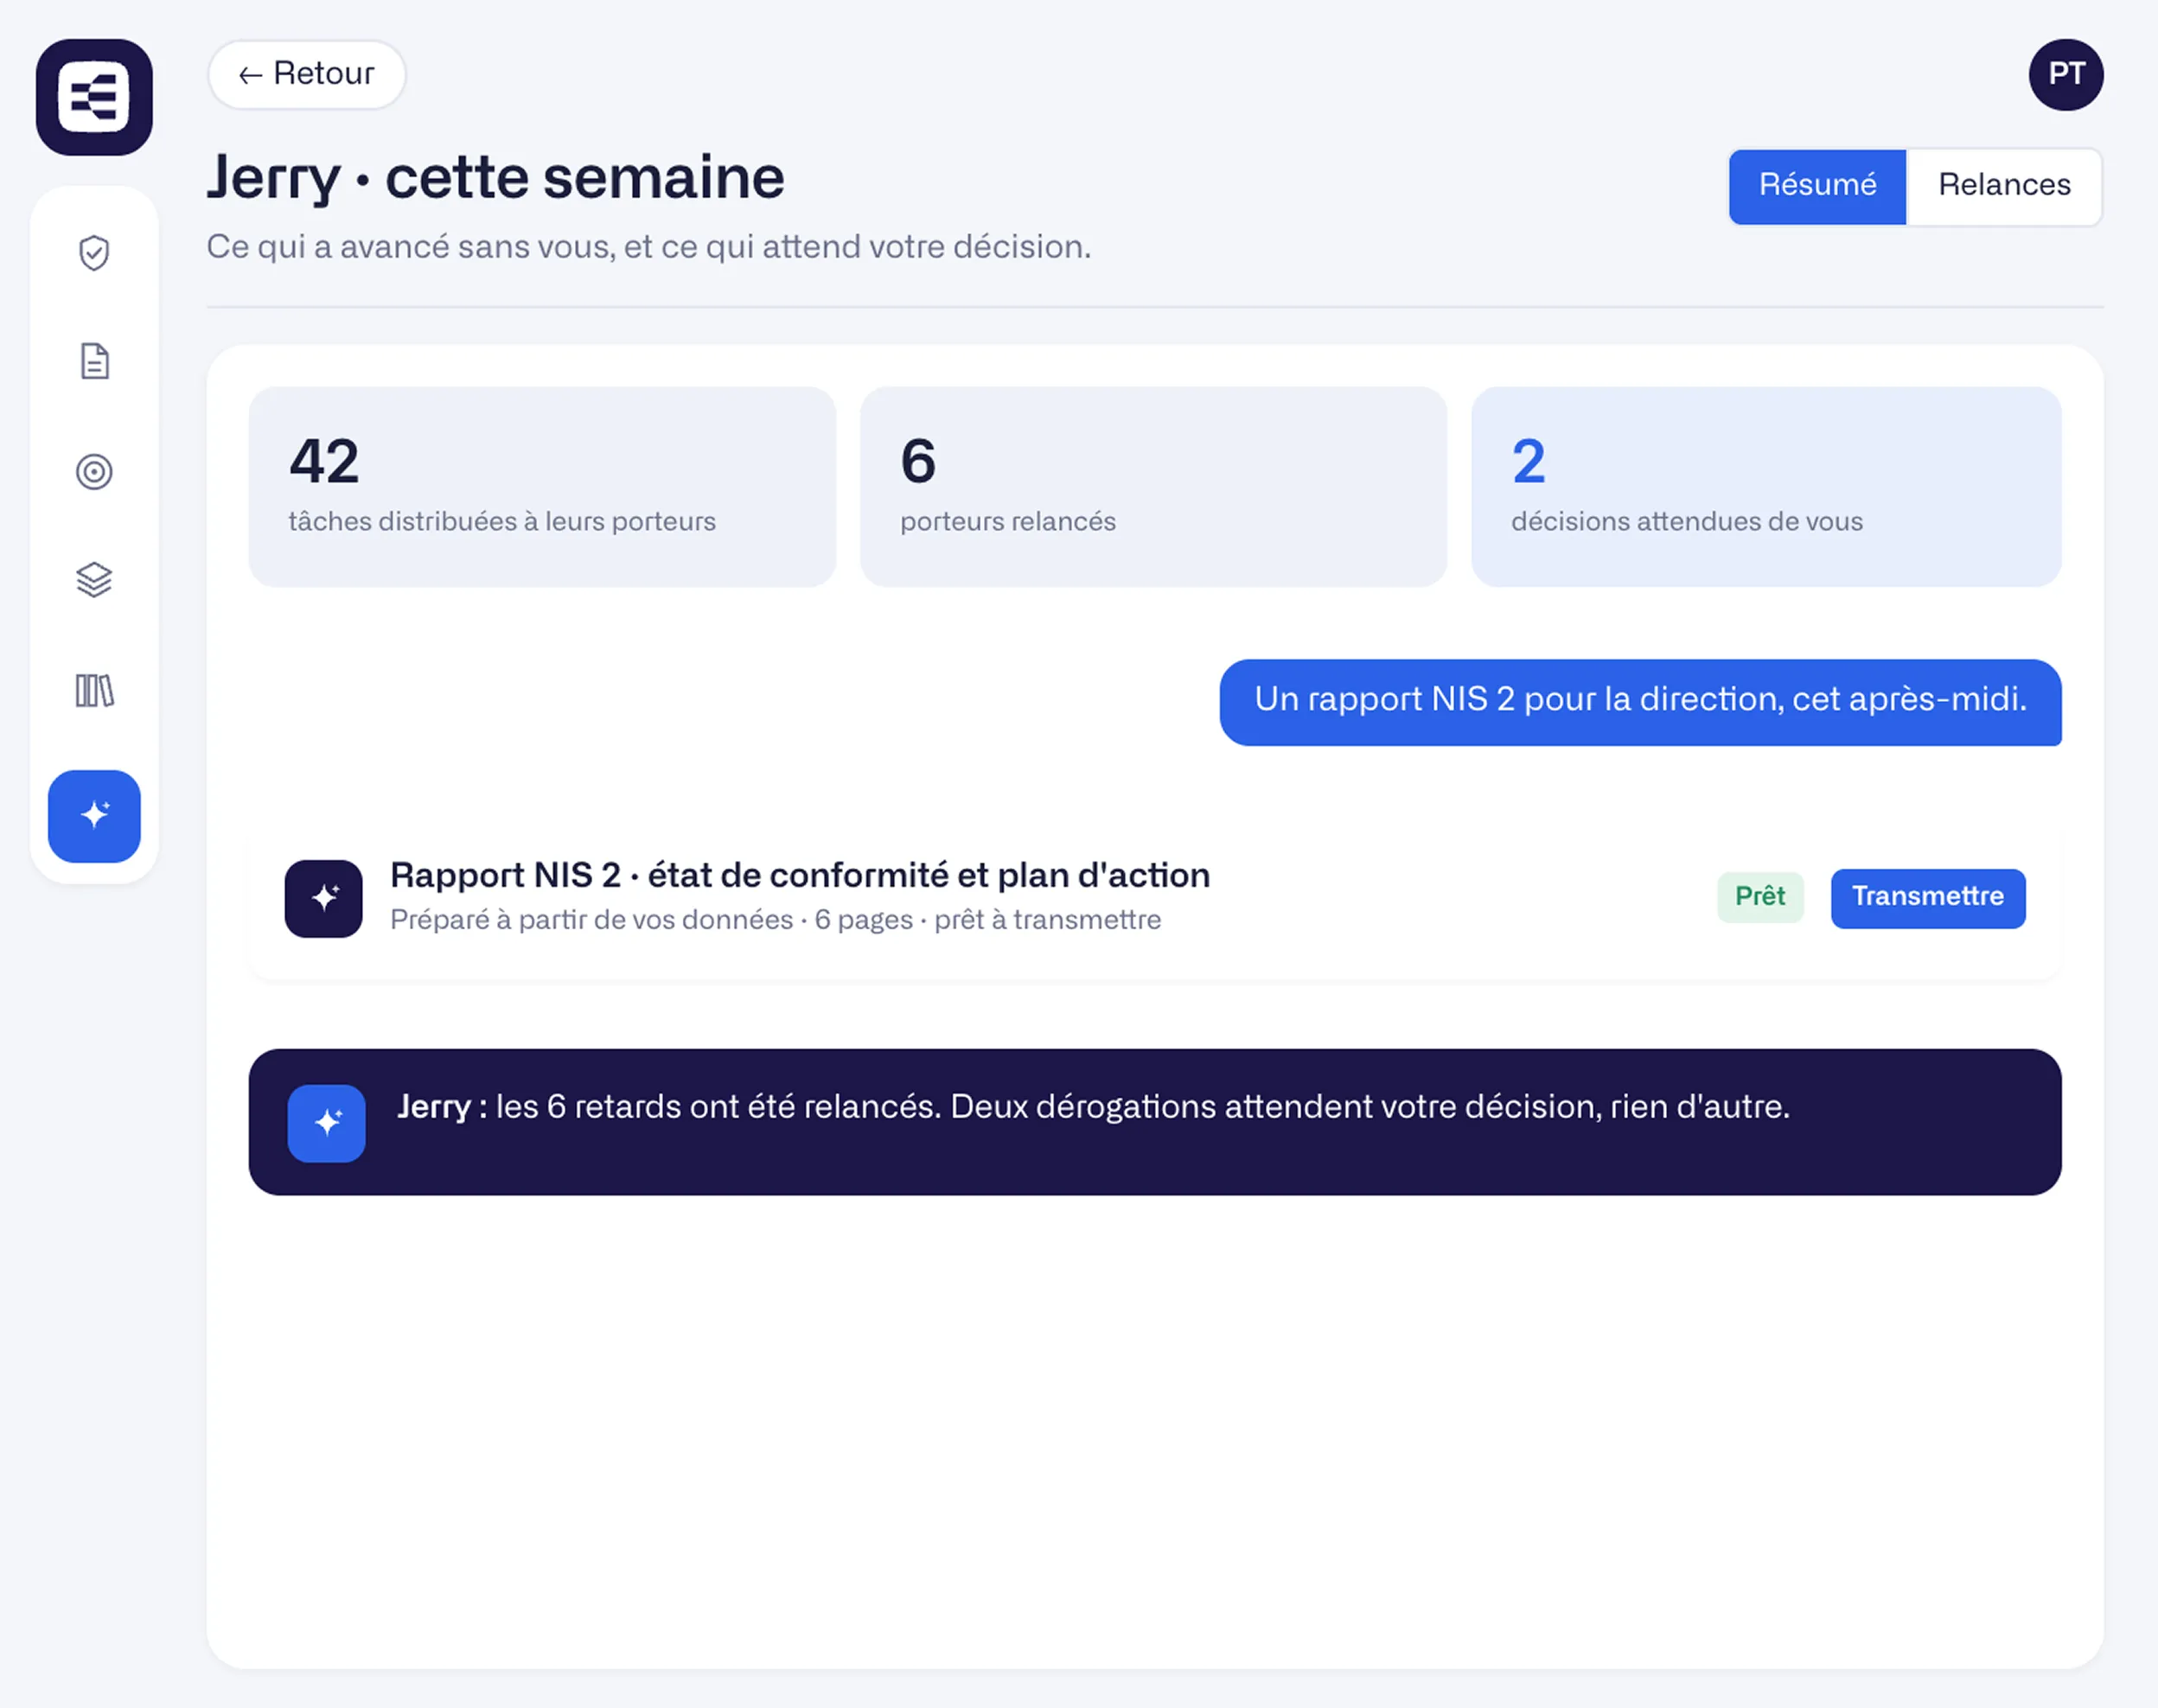
Jerry relies on this content

To link your documents, distribute tasks, and prepare your reports.   

Distributed compliance
Anticipate drift
Every action moves multiple compliance objectives forward
Prove your compliance

The platform to manage your compliance programmes

Track your compliance programmes in real time, coordinate your teams and prepare for audits with confidence, all from a single platform.

Compliance moves forward when it becomes distributed work, not a CISO-only topic.
Define roles and responsibilities once during onboarding. When a programme is created, tasks are automatically assigned based on defined domains. Every contributor has their own view and knows exactly what is expected of them.
+120 templates & resources available with unlimited access: standards, requirements, security controls, risks, vulnerabilities, support assets...
tasks distributed at programme creation
each person updates their status, submits evidence and tracks what concerns them
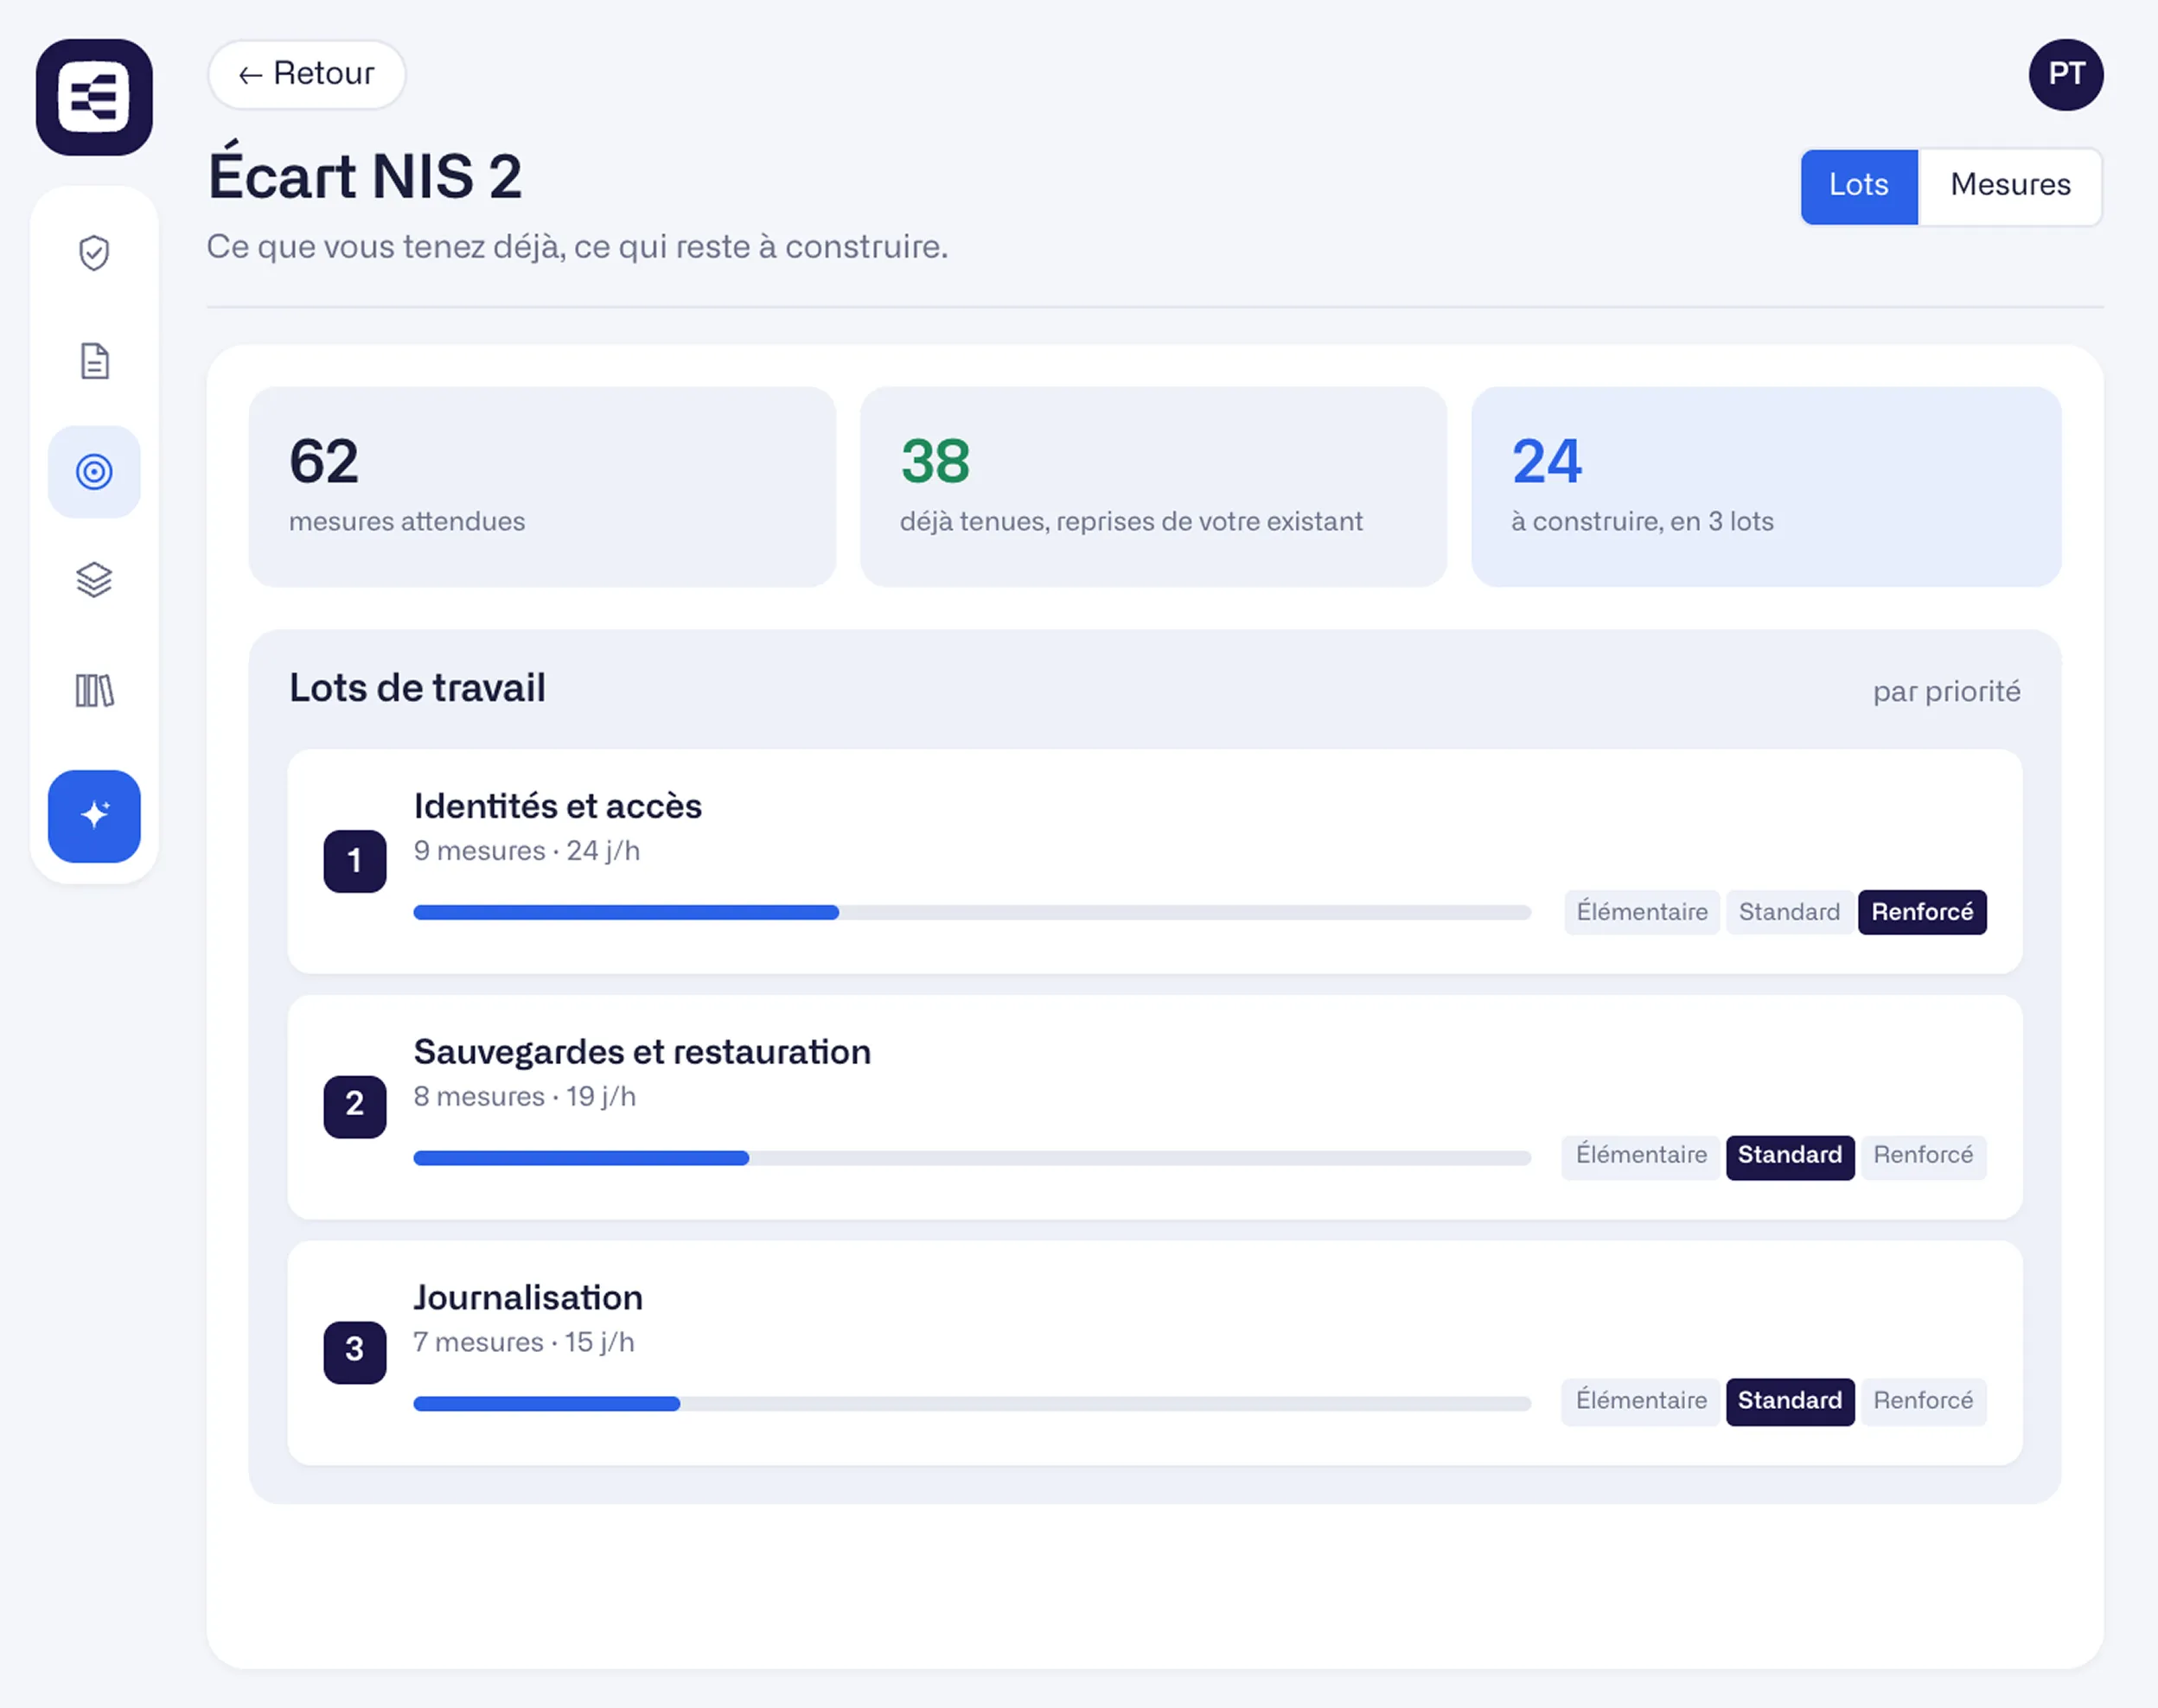
Anticipate drift before it becomes an audit delay.
Egerie continuously calculates your actual trajectory against your audit target. Lagging contributors are detected automatically and notified. You run the programme like a project manager, without having to become one.
covered / remaining / alignment with target date
potential delays identified, owners notified
requirement exclusions with tracked justification
Every action moves multiple compliance objectives forward.
A completed control automatically applies to every standard that references it. When you launch a second programme, existing work is reused, no duplication. ROI compounds with every new framework you address.
Shared controls and tasks: one control applies to multiple standards without duplication
existing work is carried over into new programmes
for each task, the impacted standards and their scores are visible, every security action contributes to multiple certifications simultaneously
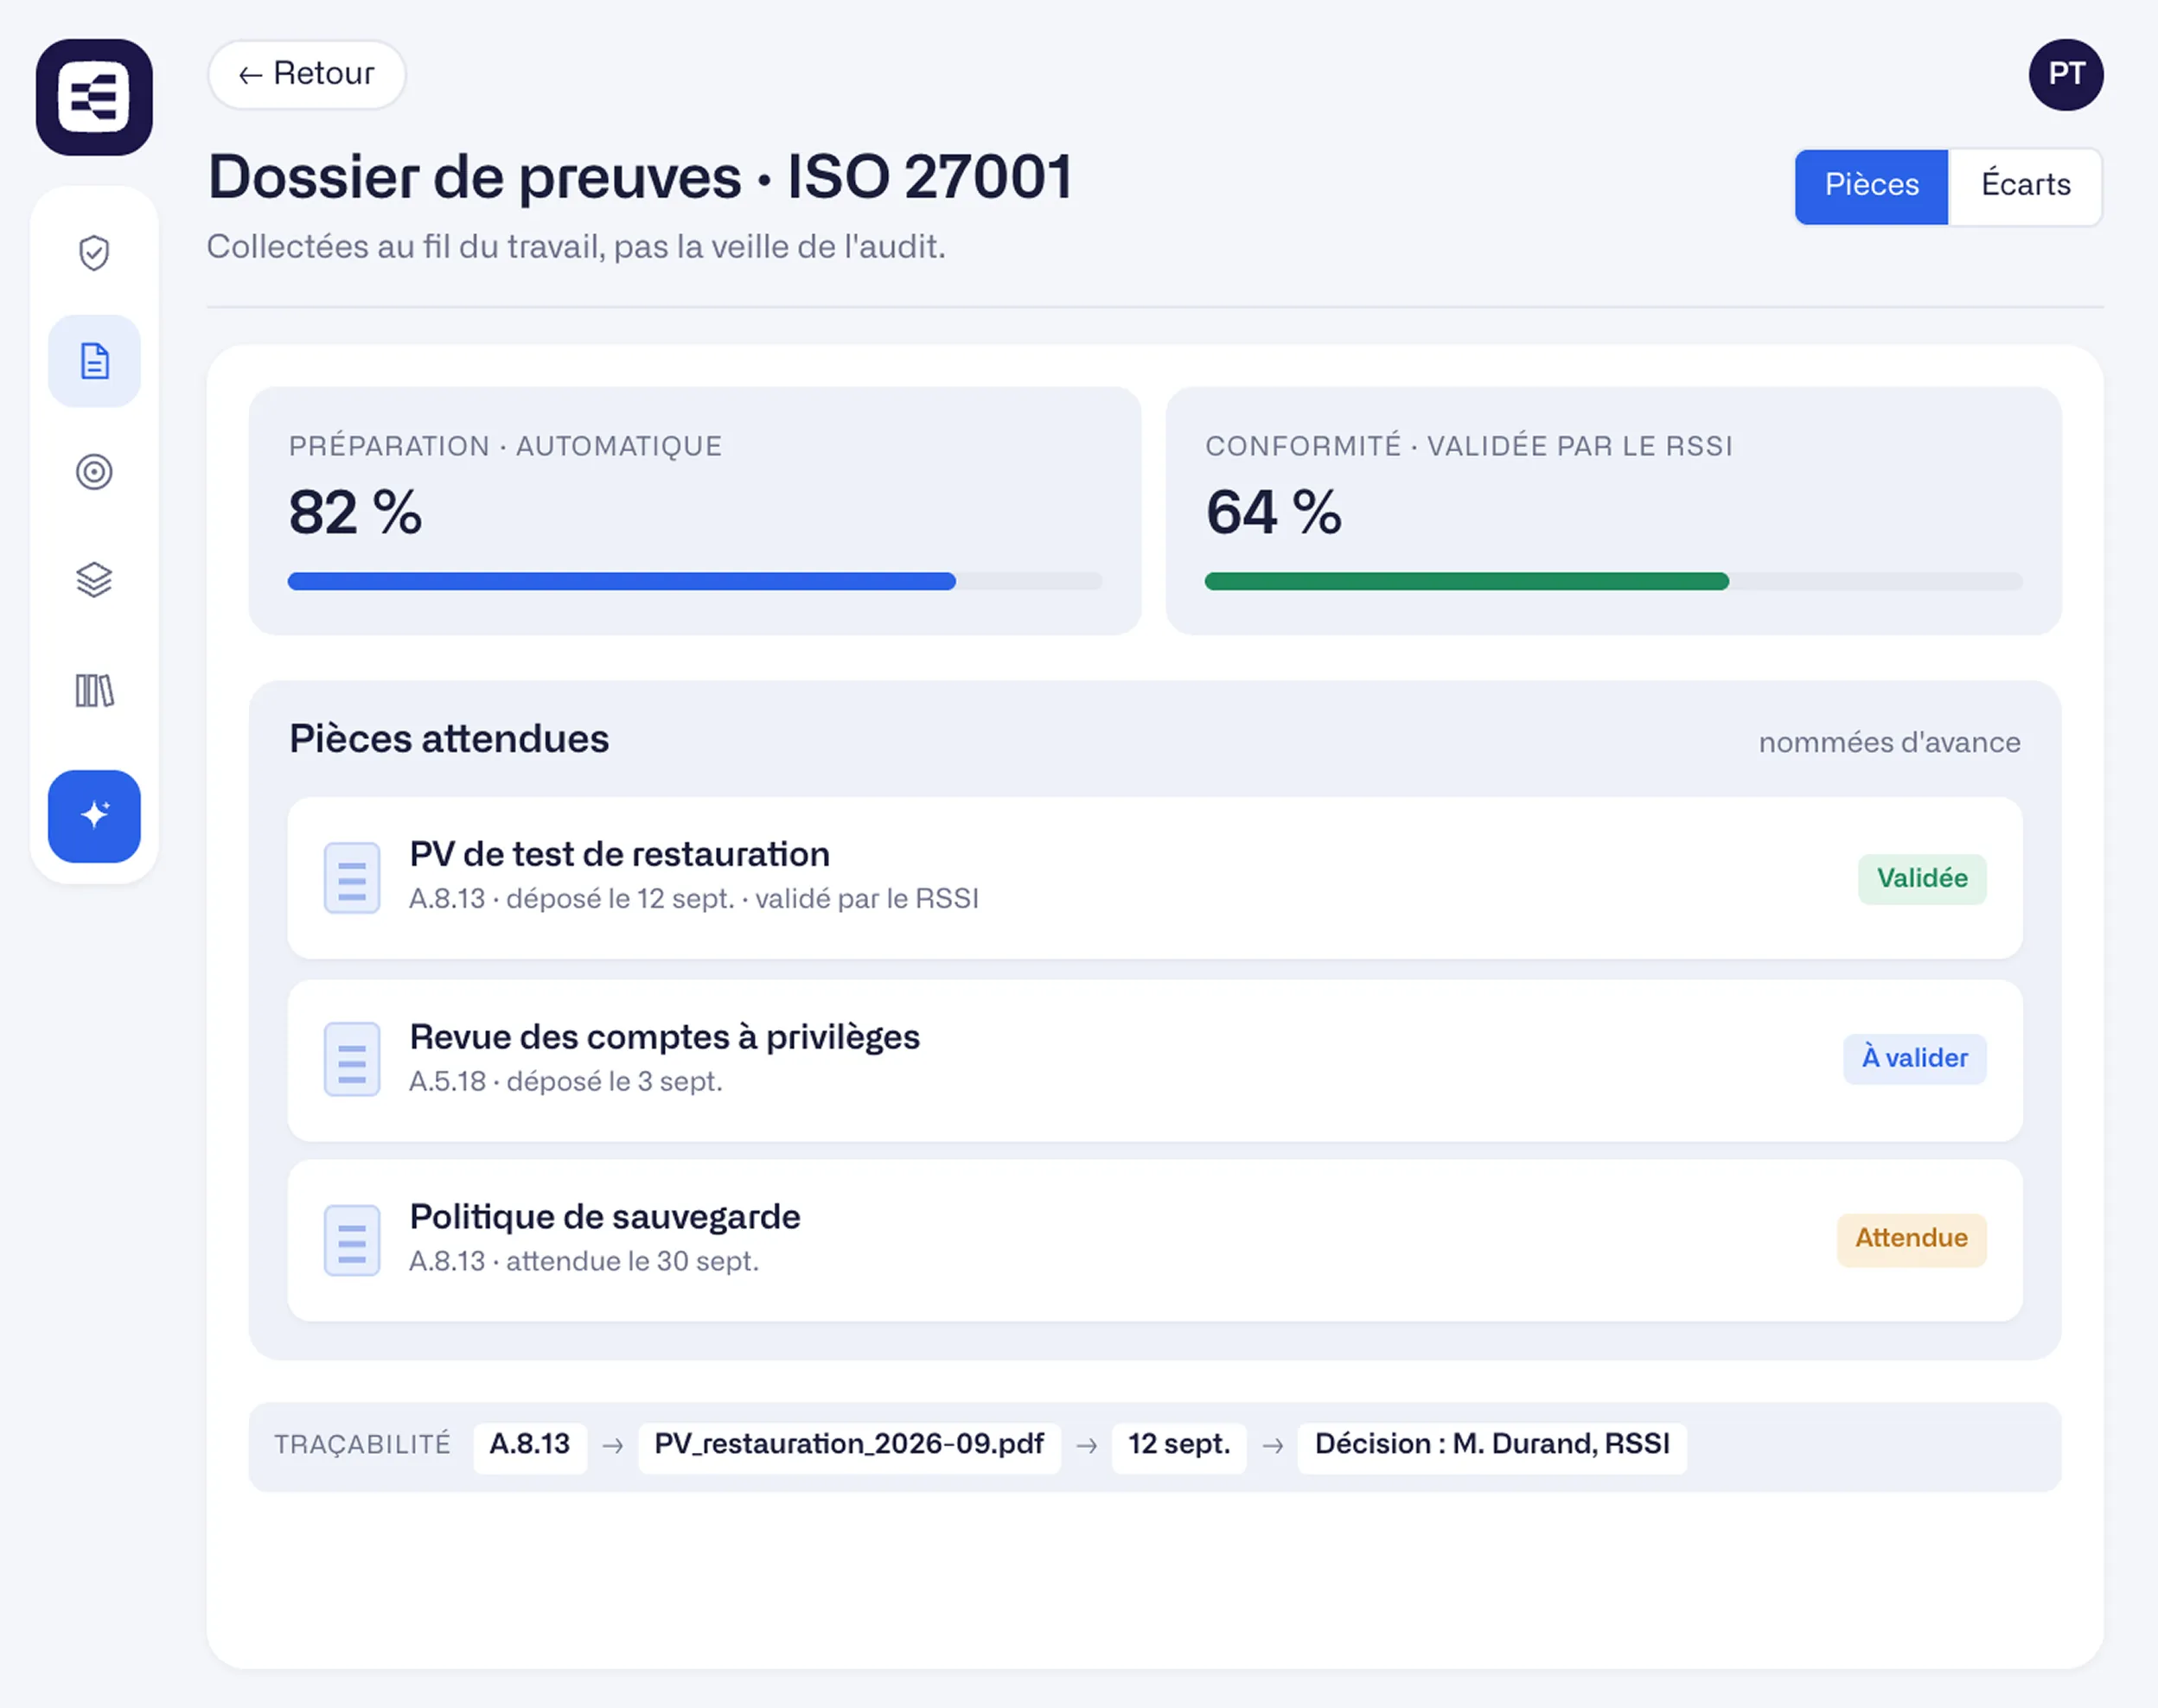
Prove your compliance, don't just declare it.
Validate, justify and accept risks in real time. Every decision is recorded with its rationale and supporting evidence. Your audit file builds continuously, not in a last-minute rush.
automatic readiness score + CISO-validated compliance score
validation, invalidation, risk acceptance with rationale and attachments
decisions, evidence, exceptions and change history, all logged
JERRY, already available

From standard to operational action,
in a matter of hours.

Reading a standard, deducing the measures, prioritizing them, and verifying that they hold up: this expertise is rare, and your experts provide it for the duration of a mission. Jerry sustains it between missions, using your own data.

Pre-configured content per standard
Egerie Content maps every standard into requirements, controls and tasks, already linked. 10+ standards, 1,000+ requirements, 3,600+ ready-to-use operational tasks.
Distributed governance from onboarding
Define roles and responsibilities once. Tasks are assigned automatically based on defined domains. Each contributor has their own view, their tasks, their evidence to submit.
Rien ne se décide sans vous
Objectif, niveau de confiance visé, acceptation d'un écart, validation d'une preuve : ces décisions portent votre nom. Chaque conclusion remonte à sa source.
TESTIMONIALS

Real stories. Real impact.

Every business has its challenges. Learn how our solutions have helped our customers overcome them and strengthen their cybersecurity.

Discover the use cases
As a major player in social protection, MGEN has transformed its cyber risk management strategy by adopting Egerie as its core GRC platform. The days of complex, rigid Excel files are gone — replaced by a streamlined, continuous approach that benefits both internal teams and external auditors, particularly in the context of ISO 27001 certification.
Florian Bourdon
Antoine Duchateau
Founder and CEO @Enteprise
MGEN: Moving Beyond Excel to Professionalize Cyber Risk Management
No Excel since the start of 2024: 100% managed in Egerie
10+ potential GRC users over time
1 single tool to centralize cyber governance
ISO 27001 audit 2024: risk management cited as a key strength by the auditor
Discover the use case
A leading financial institution in France, La Banque Postale serves individuals, businesses, and the public sector with a strong commitment to security and compliance. The organization overhauled its risk analysis methodology to improve efficiency, transparency, and its overall risk culture.
François Sopin
Antoine Duchateau
Founder and CEO @Enteprise
La Banque Postale: Scaling and Industrializing Cyber Risk Management
500+ risk analyses per year
4,996+ supporting assets identified
5,702+ security safeguards mapped
1,769 risk scenarios modeled
Discover the use case
To support its rapid growth and the growing complexity of its global supply chain, Decathlon implemented an integrated cybersecurity governance model—rooted in risk analysis and powered by the EGERIE platform.
Gaëtan Damman
Antoine Duchateau
Founder and CEO @Enteprise
Decathlon: Building a Unified, Risk-Driven Cybersecurity Approach
500+ risk analyses performed per year
4,996 assets and 5,702 security measures modeled
1,769 risk scenarios designed and evaluated
Discover the use case
How do you turn a regulatory constraint into a catalyst for cybersecurity performance? That’s the challenge the Hospices Civils de Lyon (HCL) successfully met—with support from EGERIE—by launching a project that aligned their cybersecurity practices with ISO 27001 requirements, transforming compliance into a strategic asset rather than a mere obligation.
Béatrice Berard
Antoine Duchateau
Founder and CEO @Enteprise
Turning ISO 27001 into a Strategic Opportunity: Testimony from Hospices Civils de Lyon
ISO 27001 certification achieved on the pilot perimeter, with subsequent broader rollout.
40+ risk analyses conducted and centralized
1 unified risk assessment supporting multiple frameworks (HDS, ISO 27001, etc.)
4 platform users
Discover the use case
MARKET LEADER

Recognised leader by analysts

Logo EBIQS Risk Manager avec un cercle autour du texte.
Logo Gartner Peer Insights.
Logo Gartner Cool Vendor 2023 avec texte stylisé en bleu foncé.
Logo de Gartner
Your next regulatory deadline,
as seen from your defenses

Simpler. More impact. See how we make it happen.

Request a demo