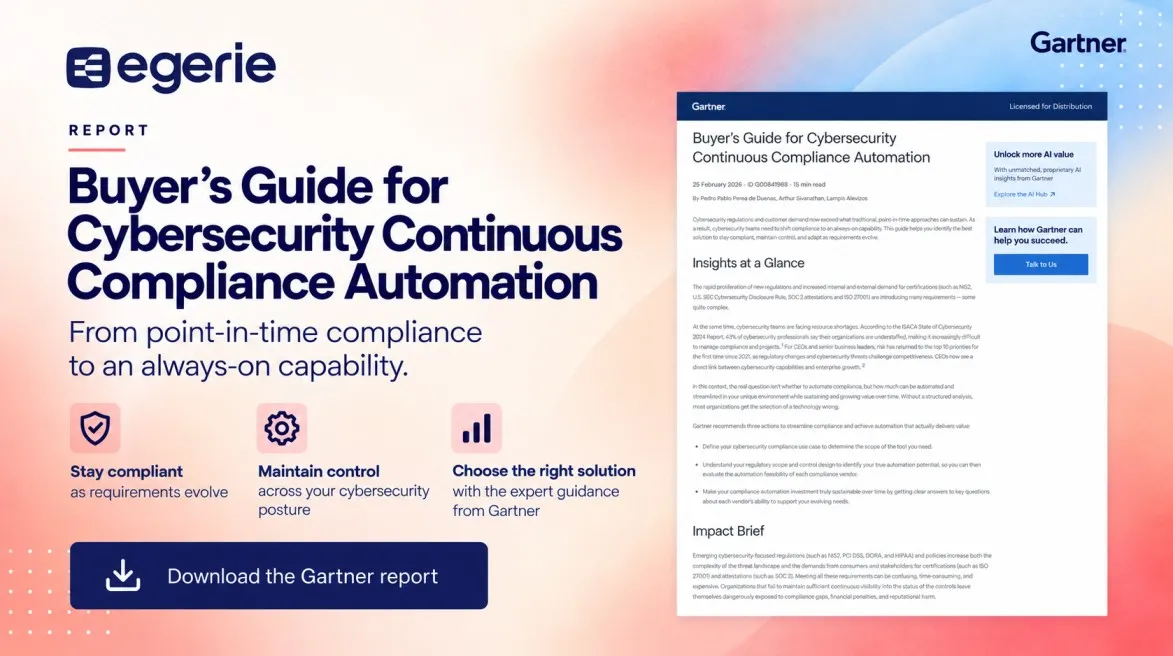
From point-in-time compliance to a permanent capability.
Cyber regulations and customer expectations are evolving faster than traditional compliance processes can keep up.
Continuous compliance automation allows cybersecurity teams to move beyond periodic assessments and manual evidence collection, adopting a more proactive and continuous approach to compliance.
This Gartner® report helps you identify the criteria to consider when choosing a continuous cybersecurity compliance automation solution, so you can stay compliant, maintain control, and adapt to changing requirements.
What you will discover in this report
- Why continuous compliance is becoming essential in the face of accelerating regulations and requirements
- How to move beyond point-in-time assessments and manual compliance processes
- Key criteria for a continuous compliance automation solution
- How to maintain visibility and control as your cyber environment evolves
- How to choose the right solution for your organization's evolving needs
Shift from periodic checks to continuous compliance
Compliance can no longer be treated as an annual exercise.
With evolving requirements and increasingly complex cyber environments, organizations need to continuously monitor their compliance posture, identify gaps, and maintain control over their obligations.
Download the Gartner® Buyer's Guide for Cybersecurity Continuous Compliance Automation to evaluate the solutions and capabilities needed for a more continuous approach to cyber compliance.
Gartner® Disclaimer
Gartner, Buyer's Guide for Cybersecurity Continuous Compliance Automation, by Pedro Pablo Perea de Duenas, Arthur Sivanathan, Lampis Alevizos, February 25, 2026.
GARTNER is a registered trademark of Gartner, Inc. and/or its affiliates.